Comparison Guide | Check Point vs. Abnormal AI
Compare Check Point and Abnormal AI for email security, AI-powered threat prevention, DLP, collaboration security and advanced cyber security capabilities.
© 2026 Check Point Software Technologies Ltd. All Rights Reserved Page 1 of 5 version_2026_v1.06 – October 23, 2026
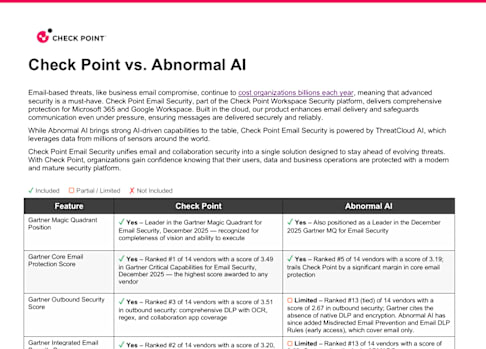
Check Point vs. Abnormal AI
Email-based threats, like business email compromise, continue to cost organizations billions each year, meaning that advanced security is a must-have. Check Point Email Security, part of the Check Point Workspace Security platform, delivers comprehensive protection for Microsoft 365 and Google Workspace. Built in the cloud, our product enhances email delivery and safeguards communication even under pressure, ensuring messages are delivered securely and reliably.
While Abnormal AI brings strong AI-driven capabilities to the table, Check Point Email Security is powered by ThreatCloud AI, which leverages data from millions of sensors around the world.
Check Point Email Security unifies email and collaboration security into a single solution designed to stay ahead of evolving threats. With Check Point, organizations gain confidence knowing that their users, data and business operations are protected with a modern and mature security platform.
✓ Included ▢ Partial / Limited ✗ Not Included
Feature Check Point Abnormal AI
Gartner Magic Quadrant Position
✓ Yes – Leader in the Gartner Magic Quadrant for
Email Security, December 2025 — recognized for completeness of vision and ability to execute
✓ Yes – Also positioned as a Leader in the December
2025 Gartner MQ for Email Security
Gartner Core Email Protection Score
✓ Yes – Ranked #1 of 14 vendors with a score of 3.49
in Gartner Critical Capabilities for Email Security, December 2025 — the highest score awarded to any vendor
✓ Yes – Ranked #5 of 14 vendors with a score of 3.19;
trails Check Point by a significant margin in core email protection
Gartner Outbound Security Score
✓ Yes – Ranked #3 of 14 vendors with a score of 3.51
in outbound security: comprehensive DLP with OCR, regex, and collaboration app coverage
▢ Limited – Ranked #13 (tied) of 14 vendors with a
score of 2.67 in outbound security; Gartner cites the absence of native DLP and encryption. Abnormal AI has since added Misdirected Email Prevention and Email DLP Rules (early access), which cover email only.
Gartner Integrated Email Security Score
✓ Yes – Ranked #2 of 14 vendors with a score of 3.20,
reflecting Check Point’s integrated platform approach across email and collaboration
▢ Limited – Ranked #13 of 14 vendors with a score of
2.66; Gartner cites the lack of DMARC management, MTA functionality and on-premises deployment options
Phishing Detection ✓ Yes – Uses many advanced AI detection engines, AI
textual analysis (NLP), user collaboration history, and machine learning to accurately block phishing (including evasive phishing, zero-day attempts, and social engineering) before attacks reach the inbox. Check Point delivers 99.7% phishing prevention, including highly sophisticated attacks.
✓ Yes – Detects phishing attacks using behavioral AI to
identify anomalies and social engineering tactics. Excels at catching sophisticated spear phishing that traditional filters might miss.
Malware & Attachment Defense
✓ Yes – Analyzes all attachments via Check Point's
ThreatCloud AI sandbox (Threat Emulation) before delivery. ThreatCloud AI combines 50+ AI engines with intelligence shared across Check Point’s network, cloud, endpoint and email security products to provide advanced pre-delivery malware protection.
▢ Mostly – Abnormal AI protects against malicious
attachments using behavioral and sender signals. However, Gartner rates Abnormal’s artifact analysis for files and attachments a relative weakness (3.7 vs. Check Point’s 4.2), and Abnormal does not publish a native sandboxing engine for novel malware or file-based zero- day attacks.
Pre-Delivery Email Blocking ✓ Yes – Inline via mail flow (transport) rules and API.
Check Point Email Security hooks into the mail flow via transport rules and API, intercepting emails before delivery with no MX record change. Detect & Remediate mode is an option for API-only protection. Prevent (inline) mode holds and analyzes messages in real time; messages deemed malicious are never delivered (they are quarantined pre-delivery). This mode also leverages the API connection to perform automated post-delivery remediation when necessary.
▢ Limited – Abnormal AI’s primary protection is API-
based and post-delivery. Its own FAQ describes deployment as API-only with “no mail-flow rerouting,” so threats are removed after they reach the inbox, leaving a dwell window that depends on API timing and message volume. Connector-based pre-delivery scanning (Exchange connector and mail flow rule, 2026) covers only auto-forwarded mail and Google collaborative inboxes. Abnormal’s “before delivery” marketing is not backed by a general inline mode for user mailboxes.
https://www.checkpoint.com/cyber-hub/threat-prevention/what-is-email-security/business-email-compromise-bec/#:~:text=A%20BEC%20attack%20takes%20advantage%20of%20a,are%20performing%20a%20legitimate%2C%20authorized%20business%20transaction.
© 2026 Check Point Software Technologies Ltd. All Rights Reserved Page 2 of 5 version_2026_v1.06 – October 23, 2026
Feature Check Point Abnormal AI
BEC & Social Engineering ✓ Yes – Protects against BEC by analyzing context and
communication behavior. Flags CEO fraud, fake invoicing, and impersonation in both emails and chats. Monitors unusual senders or requests that indicate social engineering. Analyzes user collaboration history and behavior for advanced BEC 2.0 and BEC 3.0 triggers (part of anomaly detection).
✓ Yes – Strong focus on business email compromise
(CEO fraud, supplier invoice scams, impersonation, etc.) via behavioral analysis of typical communication patterns. Provides superior protection against impersonation and socially engineered attacks.
Post-Delivery Remediation ✓ Yes – Check Point will automatically retroactively
remove or modify emails in users' mailboxes if a threat is discovered after delivery. This includes emails discovered with updated threat intelligence, click-time protection (URL defense), user reported phishing (semi- automatic and automatic handling included).
✓ Yes – Designed for continuous post-delivery detection
and remediation. It can automatically remove or quarantine emails from inboxes after delivery upon detecting a threat. Because protection is API-dependent, remediation timing depends on API call availability and message volume.
Custom Policies & Controls ✓ Yes – Provides policy configuration for each
protected app (email or collaboration). Admins can set DLP rules, adjust phishing detection aggressiveness, manage allow/block sender lists, and configure notification workflows. The interface allows both simple and advanced policy controls (as reflected by quick deployment defaults and more granular options). Set and forget it global policies are absolutely supported.
▢ Mostly – Abnormal AI’s Control Center (2026) adds
no-code custom AI models and custom rules (early access) with multi-attribute conditions. Abnormal does not function as an MTA, so traditional mail routing rules and granular delivery policies are not available.
Spam & Graymail Filtering ✓ Yes – Intercepts emails via pre-delivery or API and
analyzes content using ThreatCloud AI intelligence. Features anti-spam and reputation checks to filter junk mail before delivery, powered by Check Point's threat database. Graymail policy offers flexible options: route to junk, promotional, or custom folders, or take no action. Trusted senders can be learned automatically from user behavior. Customizable based on organizational needs across divergent groups or business units.
▢ Mostly – Relies on Microsoft/Google native email
filters for bulk spam; Abnormal AI does not provide a dedicated gateway for bulk email filtering. Abnormal does provide graymail mitigation, moving messages into a promotions folder or label post-delivery via API.
AI Textual Analysis / NLP engine
✓ Yes – Both vendors use NLP to analyze email body
text, intent, and tone. Check Point combines this with collaboration graph history and external signals.
✓ Yes – Abnormal AI also uses NLP and behavioral
signals (its behavioral model and identity trust graph), but lacks the cross-vector external telemetry of Check Point ThreatCloud AI.
Threat Intelligence & Research
✓ Yes – Leverages Check Point's ThreatCloud AI
intelligence network (a global repository of threat data from firewalls, endpoints, networks, and cloud security platforms). Incorporates up-to-date threat indicators (malicious IPs, URLs, file hashes) into email and collaboration protection, with ThreatCloud AI enrichment of indicators inside incident investigations. Provides real- time alerts and analytics to admins.
▢ Limited – Abnormal AI publishes threat research and
offers ThreatBase IP lookups, but its telemetry is limited to email and identity signals rather than network, endpoint and cloud sources.
Sender Authentication Enforcement
(SPF / DKIM / DMARC)
✓ Yes – Full support for SPF, DKIM, and DMARC
inbound authentication verification and anti-spoofing enforcement. Outbound domain management, hosted SPF/DKIM records and DMARC reporting are available with the DMARC Management add-on.
▢ Limited – Relies on the underlying email platform
(e.g., Microsoft 365) to perform SPF/DKIM checks and DMARC policy actions; custom rules (early access) can act on authentication results. Gartner notes Abnormal lacks DMARC management, and it does not provide DMARC reporting tools.
Data Loss Prevention (DLP) ✓ Yes – Provides DLP across email and connected
cloud collaboration apps (Complete Protect). Check Point DLP includes blocking with education options, manager approval workflows, and auto-encryption options for outbound protection. Encryption may be achieved with Check Point Email Encryption or Microsoft Purview (OME) enforcement. Check Point DLP is also available for Teams, OneDrive, SharePoint, Box, Dropbox, Google Drive, and Slack.
▢ Limited – Abnormal AI introduced Email DLP Rules
(early access, 2026) with regex, keyword and OCR-based detection for outbound email. Coverage is email-only, with no DLP for collaboration apps and no native encryption action.
© 2026 Check Point Software Technologies Ltd. All Rights Reserved Page 3 of 5 version_2026_v1.06 – October 23, 2026
Feature Check Point Abnormal AI
Email Encryption ✓ Yes – Check Point Email Security provides multiple
options for end-to-end message encryption. Organizations may use Check Point to enforce Microsoft Purview encryption or Check Point’s own email encryption service; for Google Workspace, Check Point email encryption is available. AI phishing detection also extends to encrypted emails.
✗ No – Does not offer an email encryption service. Secure messaging or encryption must be handled by the base email platform (e.g. Microsoft 365 Message Encryption) or a separate product.
Collaboration & SaaS App Protection
✓ Yes – Broad multi-app coverage in one platform.
Check Point secures not just email but also file-sharing and collaboration apps, scanning OneDrive, SharePoint, Google Drive, Box, Dropbox, Slack, Microsoft Teams (including tenants without E5 licensing), and more for malware, phishing, and data leakage, with CDR for OneDrive and SharePoint files.
▢ Limited – Abnormal AI’s Messaging Security scans
Microsoft Teams, Slack and Zoom messages for malicious URLs and high-risk files. It does not scan file- sharing platforms such as SharePoint, OneDrive, Google Drive, Box or Dropbox, and provides no collaboration DLP.
Account Takeover Protection
✓ Yes – Built-in account takeover prevention, included
in all plans. Check Point monitors over 100 event indicators across user login behavior and mailbox activity for signs of compromise, with the ability to block compromised accounts.
✓ Yes – Abnormal AI correlates sign-in signals (location,
device, IP) with mailbox-rule changes and can remediate automatically (sign out sessions, block, force password reset). Identity Threat Protection (2026) extends coverage to identity posture.
Security Awareness Training ✓ Yes – (Add-on) Integrated phishing simulation and
Security Awareness Training managed from the same Check Point portal. Check Point can automatically generate realistic phishing simulations and deliver training content, including a new supply chain security module.
✓ Yes – (Add-on) Abnormal AI offers AI Phishing Coach,
with phishing, BEC and QR-code simulations and AI- generated training content.
APIs and SIEM Integration ✓ Yes – Allows secure connection through a full REST
API for managing and querying security events. Easy integration is supported for SIEM, SOAR, XDR, and other platforms, including a plug-and-play CrowdStrike Falcon Next-Gen SIEM integration.
✓ Yes – Provides APIs and native integrations with
leading SIEM/SOAR platforms (e.g., Microsoft Sentinel, Splunk, Cortex XSOAR), with programmatic access to detections.
Inline Deployment Model ✓ Yes – Inline rule-based + API enabled – Check Point
uses a patented inline deployment via transport rules and API, with no MX record change.
▢ Limited – Abnormal AI is deployed primarily as a
cloud-native API app connected to Microsoft 365 or Google Workspace, with no MX record changes. Inline routing is limited to scoped paths: auto-forwarded mail, Google collaborative inboxes and the Misdirected Email SMTP relay. There is no general inline prevention mode for user mailboxes, and on-premises hybrid mailboxes remain on Abnormal’s roadmap.
Uptime & Dependency Fail Open Mechanisms
✓ Yes – Check Point email security integrates with
Microsoft 365 and Google Workspace, using its high- availability cloud to boost security without replacing email delivery. It augments the provider’s functionality, ensuring continuity.
If disrupted, Check Point fails open, reverting mail flow to the native provider (e.g., Office 365 or Gmail). As a non-MX host, it ensures uninterrupted delivery and security, enhancing reliability without risking message loss.
✓ Yes – Abnormal AI integrates with Microsoft 365 and
Google Workspace via API, relying on their infrastructure for email flow and uptime. As an add-on, it enhances security with behavioral AI, complementing the provider’s core services. Since it is not the MX host, email continues to flow through Microsoft or Google during an Abnormal outage, avoiding message loss.
Microsoft Unified Experience ✓ Yes – Check Point’s patented Microsoft 365
integration stops threats pre-delivery with unified quarantine and unified detections, minimizing quarantine confusion and admin workload. Check Point Email Security efficiency stems from out-of- the-box accuracy, advanced AI, and robust pre- and post-delivery threat management, ensuring fewer user disruptions and streamlined admin processes, while end users keep a simplified Microsoft-native experience.
▢ Partial – Abnormal AI’s Quarantine Release surfaces
Microsoft-quarantined messages and Microsoft verdicts alongside Abnormal scoring, but inside Abnormal’s separate portal. Admins still manage two systems, and end users do not get a single native Microsoft quarantine experience.
© 2026 Check Point Software Technologies Ltd. All Rights Reserved Page 4 of 5 version_2026_v1.06 – October 23, 2026
Feature Check Point Abnormal AI
Mail Explorer ✓ Yes – Check Point provides advanced message trace
and search capabilities within its unified admin interface, enabling full visibility into email flow across Microsoft 365 and Google Workspace, including message metadata, security verdicts and remediation history, plus natural-language search with Infinity AI Copilot.
✓ Yes – Abnormal AI provides message search, bulk
remediation and CSV export within its Search & Respond console.
SSPM * ✓ Yes – (Add-on) Check Point’s SaaS Security Posture
Management includes continuous misconfiguration scanning across Microsoft 365 and Google Workspace, providing automated risk prioritization, fix recommendations and posture improvement over time.
✓ Yes – Abnormal AI’s Posture Management provides
continuous Microsoft 365 and Google Workspace misconfiguration checks with risk ranking and remediation guidance.
Darkweb scanning * ✓ Yes – (Add-on) Check Point’s Leaked Credentials
add-on monitors open-web and underground sources for exposed corporate credentials. Broader brand and dark web exposure monitoring is available with Check Point Exposure Management.
✗ No – Abnormal AI does not provide dark web monitoring. Customers must rely on external threat intelligence sources to track leaked credentials.
Browser Security * ✓ Yes – (Add-on) Check Point Browser Security
extends protection into the browser, blocking phishing sites, malicious downloads and credential theft attempts when links evade detection, and applies GenAI DLP to stop sensitive data from being pasted or uploaded into AI tools.
✗ No – Abnormal AI does not offer browser security or browser isolation; its URL protection is limited to link rewriting with click tracking.
End-user Quarantine Portal training
✓ Yes – Check Point provides an integrated end-user
quarantine portal and digests, with inline explanation banners and actionable release workflows for users encountering quarantined emails.
▢ Partial – Abnormal AI offers a partial experience via its
AI-powered assistant that explains email classification, but does not offer an integrated quarantine portal with decision feedback. The Abnormal approach leaves users to engage with suspicious emails in the live inbox rather than holding them in quarantine.
Archive * ✓ Yes – (Add-on) Check Point Archiving provides
retention of up to 10 years, eDiscovery search and legal holds to meet compliance, retention and audit needs.
✗ No – Abnormal AI does not offer message archiving capabilities. Customers must retain a separate journaling or archival solution for compliance.
False Positive Auto-Restore ✓ Yes – Check Point automatically restores emails
falsely reported as phishing and supports policy-based end-user self-restore, reducing admin overhead and improving user trust.
▢ Partial – Abnormal AI’s AI Detection Engineer tunes
detections from confirmed misjudgments, but Abnormal does not publish a policy-based auto-restore mechanism; releases are handled by admins in its Search & Respond console.
Partner Risk / Supply Chain ✓ Yes – Check Point analyzes third-party email
behavior to identify compromised partners or risky supply chain patterns, offering proactive alerts and policy actions.
✓ Yes – Abnormal AI flags anomalous behavior from
external senders and provides vendor risk scoring for supply chain risk analysis.
Password Protected File Workflows
✓ Yes – Check Point identifies encrypted attachments
and applies sandboxing and content disarm workflows when passwords are extracted or provided.
▢ Limited – Abnormal AI flags password-protected
attachments based on sender and behavioral context, but does not publish password extraction or inspection of the protected file’s contents.
Shadow IT ✓ Yes – Check Point includes SaaS discovery and
shadow IT visibility in all plans, identifying unapproved applications linked to corporate credentials.
▢ Partial – Abnormal AI inventories OAuth-connected
apps with risk scoring and offers AI Governance to discover AI tools, but does not provide full SaaS shadow IT discovery.
Custom Query Exports ✓ Yes – Check Point allows direct export of alerts,
investigations and email logs via API or CSV for detailed analysis.
✓ Yes – Abnormal AI supports CSV export of search
results and dashboards, plus REST APIs for programmatic access.
© 2026 Check Point Software Technologies Ltd. All Rights Reserved Page 5 of 5 version_2026_v1.06 – October 23, 2026
Feature Check Point Abnormal AI
Security Checkup Reports ✓ Yes – Check Point provides detailed security checkup
reports with recommendations, historical data, SmartConfig security and productivity scores, and PDF generation for stakeholders and audits.
▢ Mostly – Abnormal AI provides dashboards, executive
reporting and plain-English answers via its AI Data Analyst, but does not offer a full security checkup risk assessment report.
DNS Change-log * ✓ Yes – Check Point tracks DNS records for domain
abuse, misconfiguration, or hijack attempts, logging changes over time.
✗ No – Abnormal AI does not include DNS visibility or changelog tracking features.
Smart Banners ✓ Yes – Check Point's smart banners provide inline
visual indicators for external, suspicious or spoofed senders, with admin customization, localization and sender/recipient exceptions.
▢ Limited – Abnormal AI offers end-user awareness
banners, which Gartner describes as relatively basic.
Attachment Cleaning (Threat Extraction)
✓ Yes – Check Point's Threat Extraction (CDR) strips
risky elements from attachments and delivers sanitized files (cleaned or converted to PDF) in real time, with originals recoverable when needed.
✗ No – Abnormal AI does not offer attachment sanitization. Potentially malicious documents are not cleaned before delivery.
Protect (Inline) Outgoing Traffic
✓ Yes – Check Point inspects outbound mail inline to
prevent exfiltration of sensitive content and propagation of threats.
▢ Limited – Abnormal AI can hold misaddressed
outbound emails pre-delivery via SMTP relay (Misdirected Email Prevention) and apply early-access Email DLP Rules, but does not inspect outbound mail inline for threats or malware.
Protect (Inline) Internal Traffic
✓ Yes – Check Point scans internal email flow inline to
prevent lateral movement and insider threat propagation.
▢ Partial – Abnormal AI analyzes internal-to-internal
email for lateral phishing and compromised accounts post-delivery via API; it does not scan internal mail inline.
Multi-tenant deployment ✓ Yes – Check Point provides a dedicated MSP
platform with multi-tenant management, configuration templates and delegated admin for providers managing multiple customers or business units.
▢ Partial – Abnormal AI offers multi-tenant management
for MSSPs on Microsoft 365 and Google Workspace, but does not offer a dedicated MSP platform with multi- product bundles.
Agentic AI / SOC Automation
✓ Yes – Infinity AI Copilot answers natural-language
security questions and accelerates investigations directly in the Check Point portal, alongside automated handling of user-reported emails.
✓ Yes – Abnormal AI offers AI agents for user-report
triage (AI Security Mailbox), reporting (AI Data Analyst) and detection tuning (AI Detection Engineer).
AI Usage Discovery & Governance
✓ Yes – (Add-on) Check Point Workforce AI Security
discovers sanctioned and shadow AI use across browsers, SaaS apps, desktop agents and developer tools, with coverage of tens of thousands of AI apps and AI-enabled platforms. Visibility and enforcement live in one policy engine: admins allow, coach or block by app, user and data type, write policies in plain language, and extend enforcement to the Check Point AI Network Firewall.
▢ Mostly – Abnormal AI’s AI Governance (GA, Sep
2026) discovers AI tools, tracks AI spend and uses a browser extension to flag personal-account ChatGPT use. It is a visibility and compliance-evidence layer: blocking is handed off to customer-managed workflows, and native enforcement (AI Employee Guardrails) is still in private preview.
Real-Time AI DLP / Prompt Protection
✓ Yes – Check Point inspects GenAI prompts and file
uploads in real time and blocks or coaches users before sensitive data, source code or credentials leave the organization. Enforcement covers browser, SaaS, desktop and developer AI tools, Claude Enterprise through inference hooks, and the network through the Check Point AI Network Firewall, so protection does not depend on a single extension.
▢ Limited – Abnormal AI’s AI Governance analyzes
captured ChatGPT and Claude conversations and attachments for sensitive data after it has been shared. In-the-moment blocking (AI Employee Guardrails) is in private preview with GA planned for Q4 2026, so Abnormal has no generally available real-time AI DLP today.
AI Agent & Application Security
✓ Yes – Check Point AI Application & Agent Security,
built on Lakera technology, applies runtime guardrails against prompt injection, jailbreaks and data leakage for customer-built AI apps and agents, in under 50 ms across 100+ languages. The Check Point AI Defense Plane unifies agent discovery, governance, runtime control and continuous validation, AI Red Teaming (limited release) tests AI apps, and Workforce AI Security adds prompt attack detection (early availability).
▢ Limited – Abnormal AI’s AI Agent Security (agent
inventory, access mapping and inline prompt monitoring) is in private preview, with GA planned for Q4 2026. Abnormal has no generally available runtime protection for customer-built AI applications and does not list an AI red-teaming offering.